Role-Based Access
Roles in ProNova52 are enforced at the database, not in JavaScript. Every read and write is filtered by row-level security keyed on your organisation, so a misbehaving client or third-party integration cannot cross tenancy boundaries — even by accident.
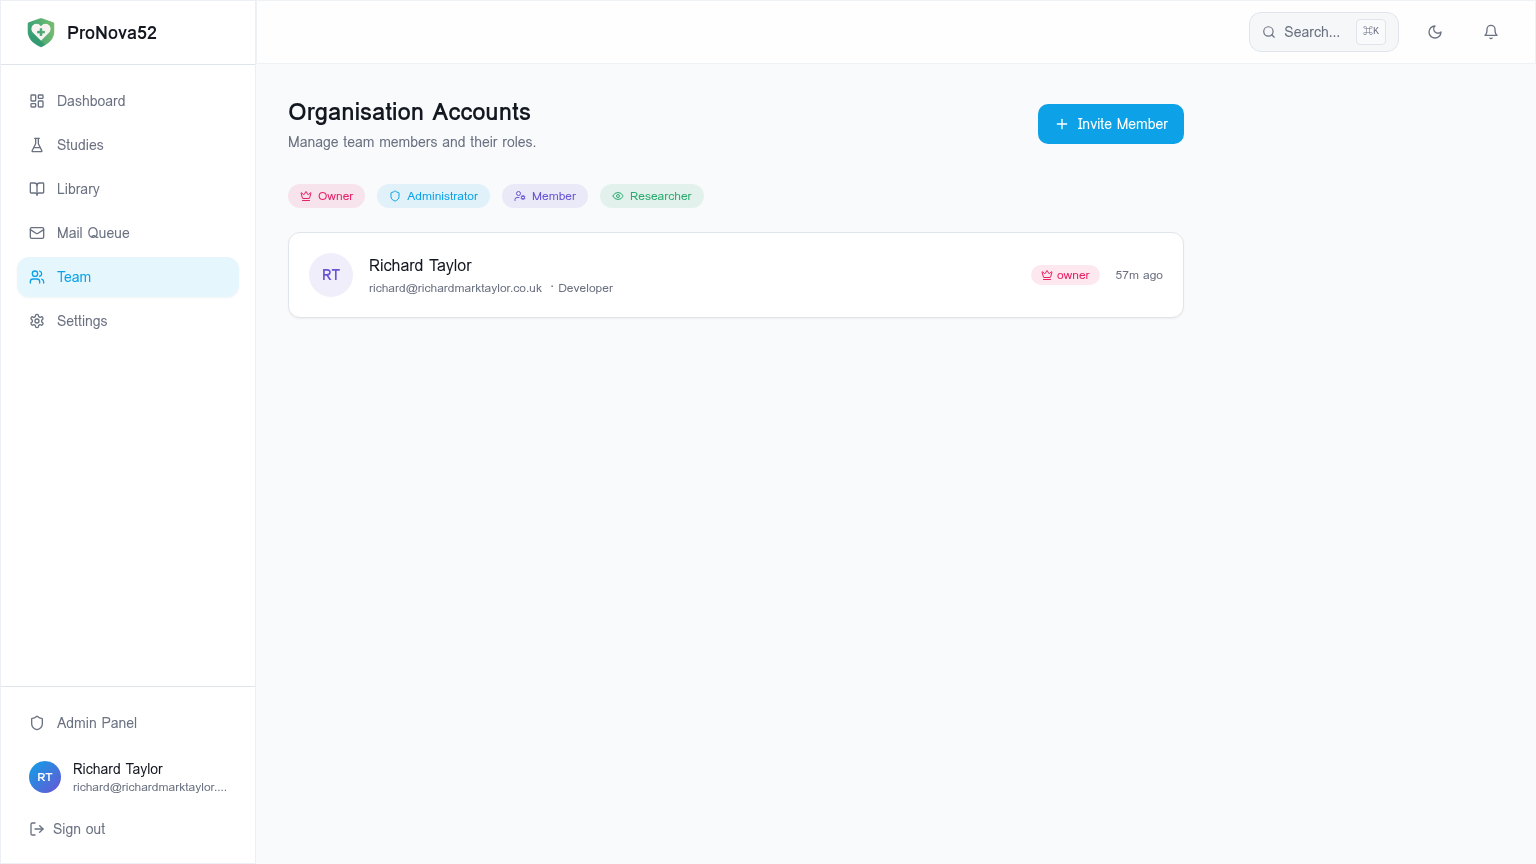
Four roles tuned for clinical teams
Owner controls billing and ownership transfer. Administrators manage studies, participants, and team membership. Members can author and edit studies but cannot manage the team. Researchers see results and responses with personal identifiers automatically masked — perfect for blinded analysis or external statisticians.
Multi-tenant by design
Every record carries an organisation_id and every query is filtered by it through PostgreSQL Row Level Security. The data model makes cross-tenant leakage structurally impossible, not merely unlikely.
Invite-only team membership
New team members join only via invitation from an Owner or Administrator, with the role they will hold defined up front. Ownership can be transferred through a dedicated, audit-logged flow.
Capabilities
- Four-tier role model: Owner, Administrator, Member, Researcher
- Database-enforced row-level security (RLS) on every table
- Researcher role with automatic PII masking
- Invite-only team onboarding with pre-assigned roles
- Audit-logged ownership transfer
- Organisation-scoped admin tooling
Typical use cases
- Multi-site studies with site-administrator delegation
- External statistician access with blinded data
- Clinical operations teams with non-clinical analysts